Solutions›
Frameworks
ISO 27001NIS2TISAX®GDPRDORANISGEU AI ActISO 9001Whistleblower Protection ActSOC 2ISO 27017ISO 27018VdS 10000VdS 10100Industry Solutions
StartupsScaleupsMid-MarketSoftware and IT ConsultingFinancial ServicesEnergyFood & BeverageHealthcareIndustry and ManufacturingLogisticsAerospace and DefenseNonprofits and NGOsMunicipal Utilities and Waste ManagementCritical Infrastructure (KRITIS)Managed Compliance
CISO as a ServiceDPO as a ServiceQuality Manager as a ServiceAI Officer as a ServiceUse Cases
Information SecurityData ProtectionQuality ManagementAI ManagementWhistleblowingBusiness Continuity ManagementSoon
Company›

Popular
Most common starting points
›

Frameworks
ISO 27001, NIS2, TISAX®, and more
›

Industry Solutions
Finance, energy, and more
›

Managed Compliance
Security, privacy, quality, and AI officers
›

Use Cases
ISMS, data protection, QMS, and more
›

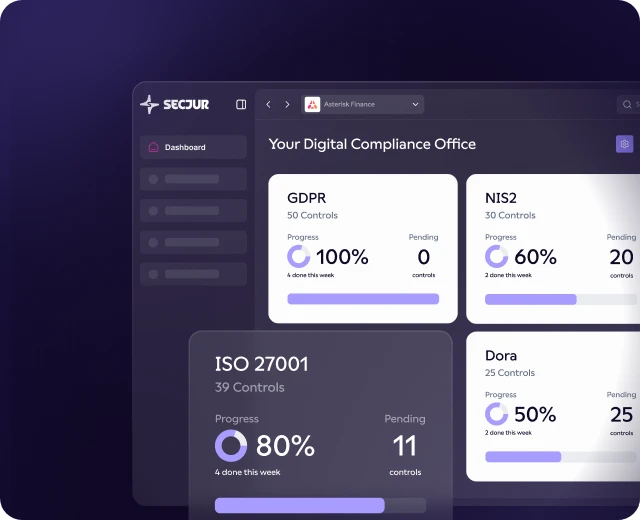
Compliance Platform
The Digital Compliance Office
›

AI FirewallNew
Use AI in line with the law
›
Popular
Frameworks
Compliance by industry
Compliance by Use Case

Industry Solutions
By industry

Software and IT Consulting

Financial Services

Energy

Food & Beverage

Healthcare

Industry and Manufacturing

Logistics

Aerospace and Defense

Nonprofits and NGOs

Municipal Utilities and Waste Management

Critical Infrastructure (KRITIS)
By size


Managed Compliance

CISO-as-a-Service
External information security officer

DPO-as-a-Service
External data protection officer

Quality Manager-as-a-Service
External quality management representative

AI Officer-as-a-Service
External AI officer
“SECJUR takes the heavy lifting in information security off our hands. We had only a few weeks until the certification audit and no one in the company to build an ISMS. Thanks to SECJUR, we still haven’t had to fill a dedicated position, and we passed the audit without any issues.”
Jan Sorgenfrei
Vice President of Engineering, Circus SE
Use Cases
ISMS
Information Security
ISO 27001, TISAX®, NIS2, and more
DPMS
Data Protection
GDPR-compliant data protection
QMS
Quality Management
ISO 9001
AIMS
AI Management
ISO 42001 and EU AI Act

Whistleblowing
Whistleblowing
Whistleblower Protection Act

BCM
Business Continuity Management
Emergency and crisis management
Your expert builds and manages your management system in the Digital Compliance Office
Save on expensive consultants and hundreds of hours of internal effort.
How It Works →
The Digital Compliance Office
A selection of modules

Navigator
Guided steps for build and operation.

Asset Management
All assets in one place, by criticality.

Risk Management
Assess, treat, and track risks.

Vendor Management
Keep service providers and suppliers in view.

Policy Management
Create, link, and approve policies.

Incident Management
Detect, classify, and report incidents.

Contract Management
Data protection agreements and DPA review.

Task Management
All tasks and deadlines at a glance.
Navigator · ISO 27001
Headquarters
Progress
80%
✓
Define scope
done
✓
Record assets
done
✓
Assess risks
done
Your expert
linked 3 pieces of evidence
And much more
Audit management, online training, records of processing, AI inventory, TOMs, and more
Explore Platform →
SECJUR AI FirewallBeta
The problem
44%
of your employees break company policy or the law when using AI.
Your team uploads confidential client and personal data to ChatGPT, Claude and co. With your permission or without.
Source: KPMG, 2025
The solution
Use AI, within your rules.
The AI Firewall checks every request right in the AI tool and says at once whether it is allowed.
Your AI assistant · Claude
Put the sick notes from the team into one table.
Checked with SECJUR AI Firewall
Not allowedRule 2.1 · No health data in AI tools
Ban AI or let it run? Both go wrong.
Explore AI Firewall →

Knowledge
Articles, guides, and glossary
›

Templates & Downloads
Whitepapers, checklists, and templates
›

Product & Help
Help center, integrations, and updates
›



 Your expert