Menu
How It WorksCustomersPartners
Popular
Most common starting points
›
Frameworks
ISO 27001, NIS2, TISAX®, and more
›
Industry Solutions
Finance, energy, and more
›
Managed Compliance
Security, privacy, quality, and AI officers
›
Use Cases
ISMS, data protection, QMS, and more
›
Compliance Platform
The Digital Compliance Office
›
AI FirewallNew
Use AI in line with the law
›
Managed Compliance

“SECJUR takes the heavy lifting in information security off our hands. We had only a few weeks until the certification audit and no one in the company to build an ISMS. Thanks to SECJUR, we still haven’t had to fill a dedicated position, and we passed the audit without any issues.”
Jan Sorgenfrei
Jan Sorgenfrei
Vice President of Engineering, Circus SE
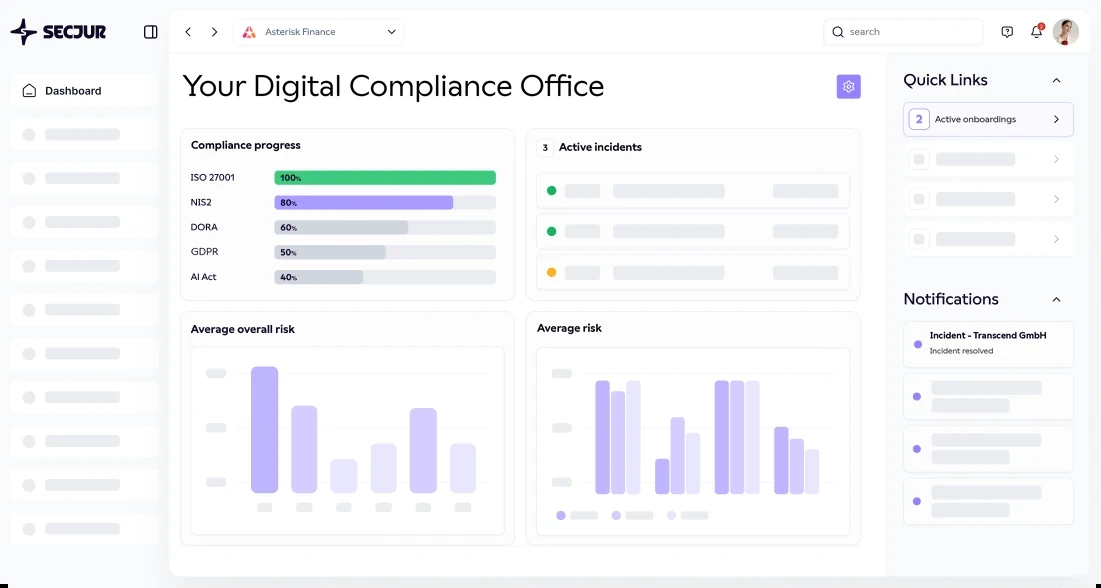
The Digital Compliance Office
A selection of modules
Navigator
Guided steps for build and operation.
Asset Management
All assets in one place, by criticality.
Risk Management
Assess, treat, and track risks.
Vendor Management
Keep service providers and suppliers in view.
Policy Management
Create, link, and approve policies.
Incident Management
Detect, classify, and report incidents.
Contract Management
Data protection agreements and DPA review.
Task Management
All tasks and deadlines at a glance.
Navigator · ISO 27001
Headquarters
Progress
80%
✓
Define scope
done
✓
Record assets
done
✓
Assess risks
done
Your expert
linked 3 pieces of evidence
And much more
Audit management, online training, records of processing, AI inventory, TOMs, and more
Explore Platform →
SECJUR AI FirewallBeta
The problem
44%
of your employees break company policy or the law when using AI.

Your team uploads confidential client and personal data to ChatGPT, Claude and co. With your permission or without.

Source: KPMG, 2025
The solution
Use AI, within your rules.

The AI Firewall checks every request right in the AI tool and says at once whether it is allowed.

Your AI assistant · Claude
Put the sick notes from the team into one table.
Checked with SECJUR AI Firewall
Not allowed
Rule 2.1 · No health data in AI tools
Ban AI or let it run? Both go wrong.
Explore AI Firewall →
Knowledge
Articles, guides, and glossary
›
Templates & Downloads
Whitepapers, checklists, and templates
›
Product & Help
Help center, integrations, and updates
›

Your external DPO

A dedicated SECJUR expert is appointed as your Data Protection Officer (DPO). Your expert builds your data protection management system according to the GDPR and the German BDSG, keeps it up to date, and advises your management.

Appointment and notification to the supervisory authority included.

✓
We do 80%
✓
Hosted in Germany
✓
ISO 27001 certified
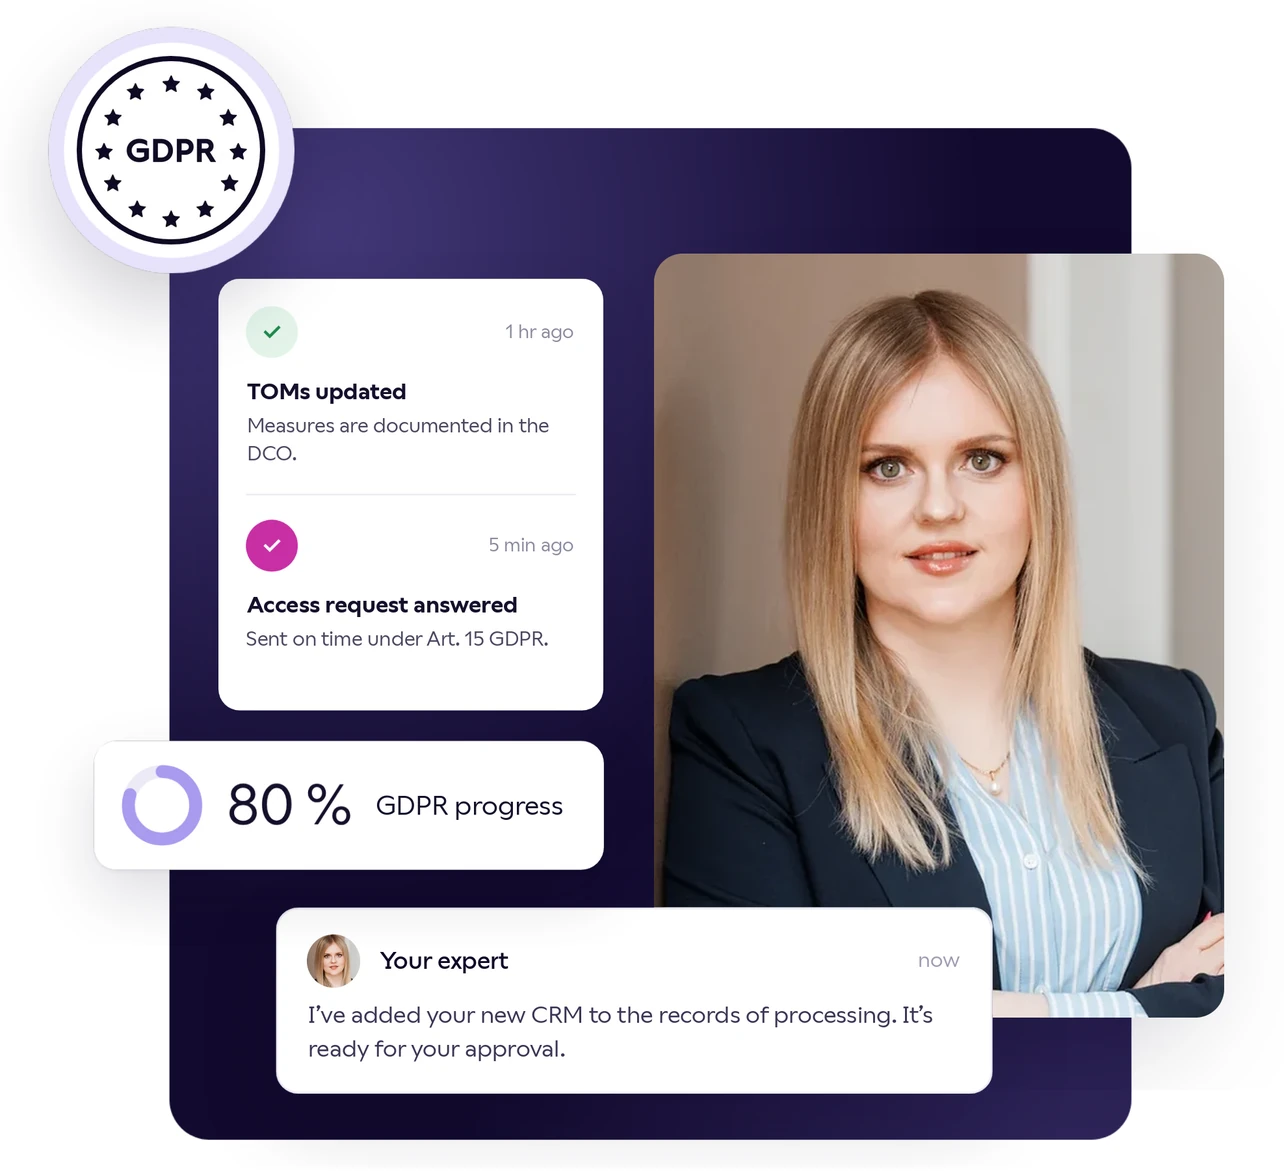
Your SECJUR expert in the DCO: GDPR progress, status updates and approvals

SECJUR customers are in good company

OTTOStahlwerk ThüringenNordzuckeryfoodStadtwerke CottbusSteyr MotorsStatista
Why SECJUR

Your DPO, without a conflict of interest

Without SECJUR
An internal DPO needs expertise and ongoing training
The role runs on the side in IT or HR
Knowledge depends on a single person
Requests and data breaches are left unresolved
Every document is created from scratch
Records of processing scattered across Word and Excel
With SECJUR
DPO-as-a-Service
A SECJUR expert is appointed and registered as your DPO
An independent DPO does 80% of the work
A dedicated DPO backed by the SECJUR team
Clear processes for requests and data breaches
Templates and automation on our platform
RoPA, TOMs, and DPAs audit-proof in the DCO
How It Works

Expert quality at AI speed

Software and expertise in one. We take on around 80% of your data protection tasks. You provide information, give approvals, and involve your organization.

✓
Our Digital Compliance Office handles the routine work
Records of processing, TOMs, DPAs, and retention periods in one place, continuously maintained
✓
Your DPO advises and monitors
Data protection impact assessments, service provider reviews, and reports to management
✓
You approve and stay audit-ready
We take care of internal data protection audits, documented in the DCO
Your SECJUR expert
Digital Compliance Office
Your expertRecords of processing

Processing activity “Applicant management” added.

12 min agoApprove
Management systems

One management system, all frameworks

01
Data protection (DPMS)

Your DPO builds a data protection management system according to the GDPR and the BDSG, and on request also for the Swiss nFADP: records of processing, TOMs, data processing, data subject requests, and data protection impact assessments.

More on data protection →
02
Information security (ISMS)

ISO 27001, NIS2, TISAX®, DORA, and SOC 2 on the same foundation. You implement technical and organizational measures once and use them for both data protection and information security.

More on information security →
03
Quality management (QMS)

ISO 9001 on the same foundation, with shared documents, audits, and management reviews.

More on quality management →
04
Whistleblowing

A secure, anonymous reporting channel in line with German and EU requirements.

More on whistleblowing →
05
AI management

EU AI Act and ISO 42001: record AI systems, assess risks, and document governance.

More on AI management →
More on the platform →
Your compliance modules
DCO
DPMS (GDPR, BDSG)
82 %
ISMS (ISO 27001, NIS2)
100 %
QMS (ISO 9001)
planned
Whistleblowing
Reporting channel active
AI management (EU AI Act)
in progress
Shared controls
reused
A.5.34 Privacy and protection of PII
ISO 27001, GDPR, TISAX®
Your experts

Real experts by your side

Your DPO is a dedicated SECJUR expert who knows data protection law and your industry and is directly available to you.

SECJUR information security expert
SECJUR expert
SECJUR information security expert
SECJUR AI management expert
SECJUR expert
SECJUR information security expert
SECJUR data protection expert
SECJUR quality management expert
Discover SECJUR →
The comparison

SECJUR compared

Internal DPO, traditional external DPO, or SECJUR: how the three paths to your Data Protection Officer compare.

Internal DPO
An employee from your own team
External DPO
Law firm or individual consultant
SECJUR DPO-as-a-Service
Platform plus dedicated expert
Who does the work
– The DPO, alongside their actual role
– The consultant advises, your team documents
✓Your DPO does 80% of the work
Cost
– Working time, training, protection against dismissal
– Flat fee plus hours per case
✓Fixed price
Availability
– Unavailable during vacation, illness, or job changes
– Only on request and within a quota
✓A dedicated DPO backed by a team
Expertise
– Depends on one person
– High, but far from day-to-day business
✓An expert who knows your industry
Documentation
– Scattered across Word, Excel, and SharePoint
– Stays with the consultant, hard to hand over
✓Centralized in the DCO, linked and versioned
Information Security
– A separate topic, often a different person
– A separate engagement
✓DPMS and ISMS on one platform
Requests and data breaches
– Dependent on one person
– Depends on the consultant’s availability
✓Clear process, deadlines in view
Success story

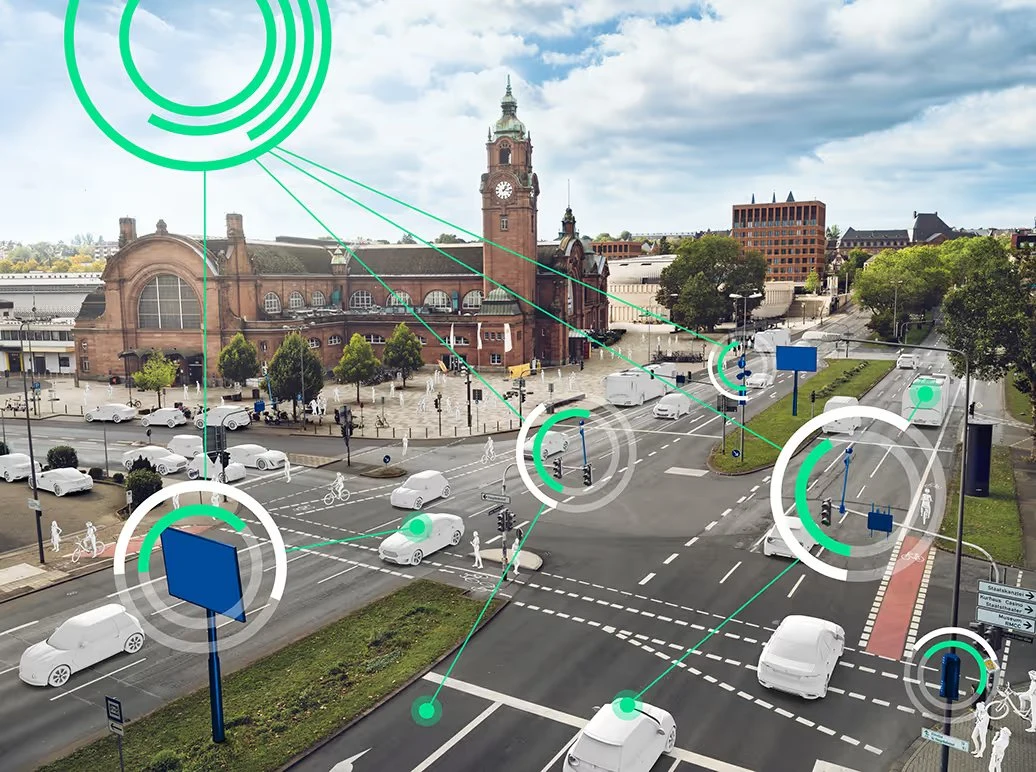
One DPO for 26 companies

Kreuzung mit vernetzter VerkehrstechnikKreuzung mit vernetzter Verkehrstechnik
Data protection structures for 26 companies in
5 months

“With SECJUR, we have found exactly what we were looking for in the area of data protection: a ‘data protection-as-a-service package’ that is ideally suited to us and meets our requirements in every respect through the combination of a team of experts with the online platform Digital Compliance Office.”

Nina Miller
Nina Miller
Yunex Traffic
FAQ

Frequently asked questions

Request a Quote →
Do we even need a Data Protection Officer?
+

In Germany, generally from 20 people who constantly process personal data by automated means (Section 38 BDSG). Part-time staff and trainees count. Regardless of headcount, the obligation applies if your processing requires a data protection impact assessment.

What internal resources do I need?
+

We take on 80% of the data protection effort. You need an internal coordinator who knows your processes and reports new projects, service providers, or requests to your DPO early.

Is the external DPO liable for data protection?
+

No. Your company remains responsible, and your management makes the decisions. Your DPO advises, monitors compliance with the GDPR, and is the point of contact for the supervisory authority and data subjects.

What happens in the event of a data breach?
+

You report the incident through the Digital Compliance Office. Your DPO assesses whether there is a reporting obligation and prepares the notification to the supervisory authority and, if necessary, to the data subjects. A 72-hour deadline applies.

We already have a DPO. How does the switch work?
+

Your new DPO moves the existing documents into the Digital Compliance Office, checks them for gaps, and notifies the supervisory authority of the change.

Get started

Bring your DPO onto the team

Book an Intro CallHow It Works
Your DPO at a fixed price
Your DPO does 80%
Request a Quote