Menu
How It WorksCustomersPartners
Popular
Most common starting points
›
Frameworks
ISO 27001, NIS2, TISAX®, and more
›
Industry Solutions
Finance, energy, and more
›
Managed Compliance
Security, privacy, quality, and AI officers
›
Use Cases
ISMS, data protection, QMS, and more
›
Compliance Platform
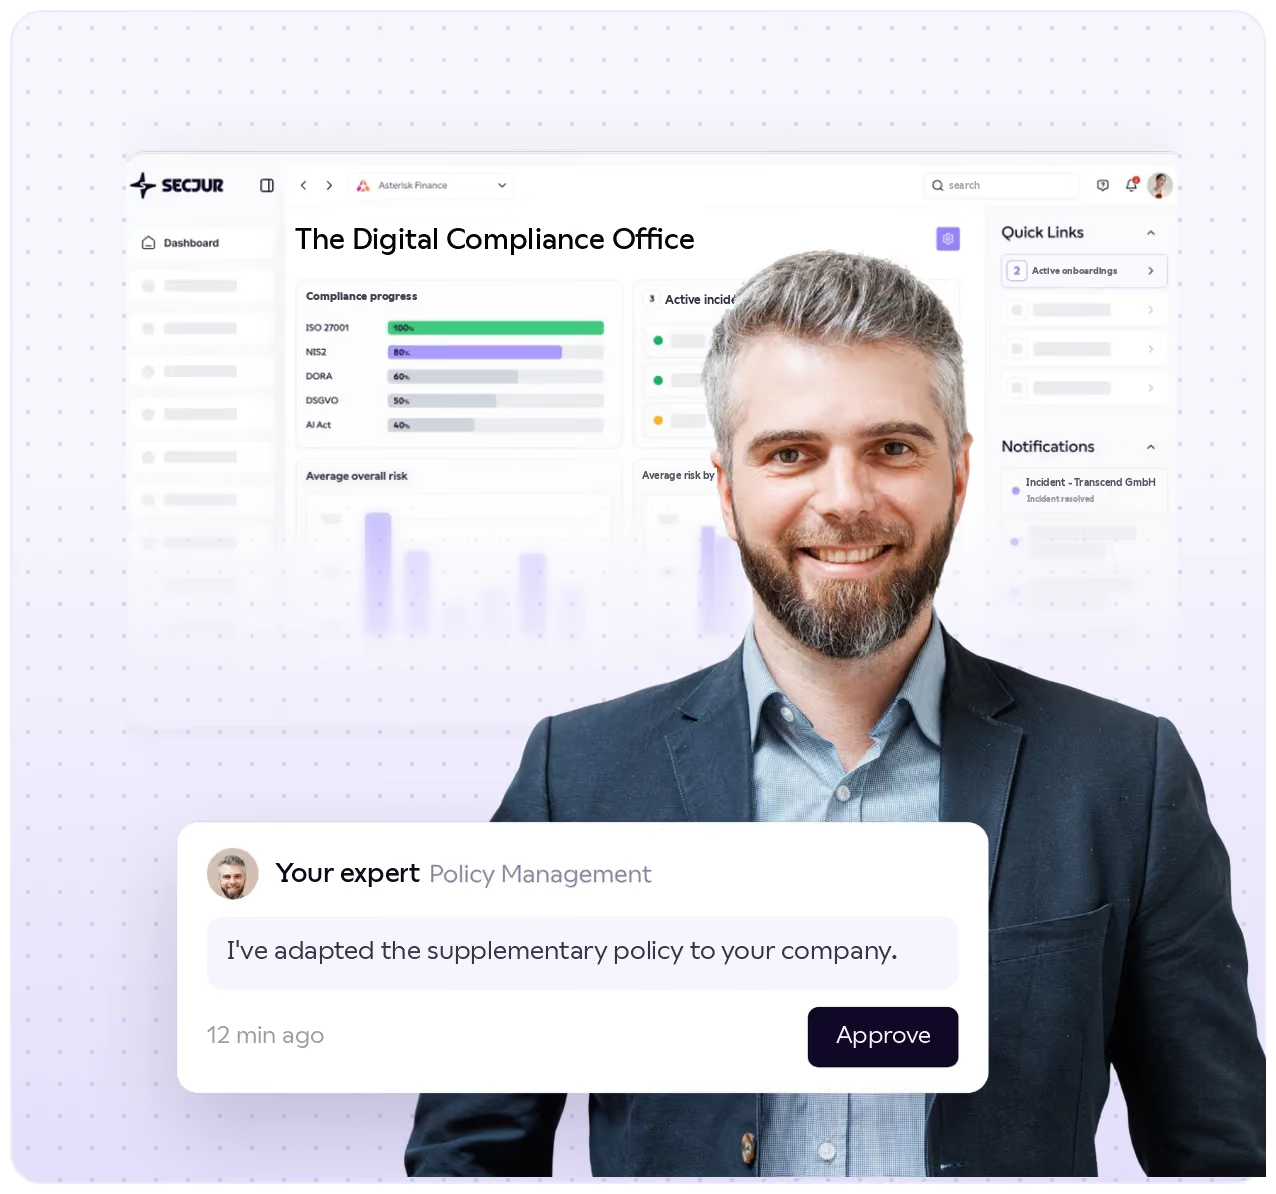
The Digital Compliance Office
›
AI FirewallNew
Use AI in line with the law
›
Managed Compliance

“SECJUR takes the heavy lifting in information security off our hands. We had only a few weeks until the certification audit and no one in the company to build an ISMS. Thanks to SECJUR, we still haven’t had to fill a dedicated position, and we passed the audit without any issues.”
Jan Sorgenfrei
Jan Sorgenfrei
Vice President of Engineering, Circus SE
The Digital Compliance Office
A selection of modules
Navigator
Guided steps for build and operation.
Asset Management
All assets in one place, by criticality.
Risk Management
Assess, treat, and track risks.
Vendor Management
Keep service providers and suppliers in view.
Policy Management
Create, link, and approve policies.
Incident Management
Detect, classify, and report incidents.
Contract Management
Data protection agreements and DPA review.
Task Management
All tasks and deadlines at a glance.
Navigator · ISO 27001
Headquarters
Progress
80%
✓
Define scope
done
✓
Record assets
done
✓
Assess risks
done
Your expert
linked 3 pieces of evidence
And much more
Audit management, online training, records of processing, AI inventory, TOMs, and more
Explore Platform →
SECJUR AI FirewallBeta
The problem
44%
of your employees break company policy or the law when using AI.

Your team uploads confidential client and personal data to ChatGPT, Claude and co. With your permission or without.

Source: KPMG, 2025
The solution
Use AI, within your rules.

The AI Firewall checks every request right in the AI tool and says at once whether it is allowed.

Your AI assistant · Claude
Put the sick notes from the team into one table.
Checked with SECJUR AI Firewall
Not allowed
Rule 2.1 · No health data in AI tools
Ban AI or let it run? Both go wrong.
Explore AI Firewall →
Knowledge
Articles, guides, and glossary
›
Templates & Downloads
Whitepapers, checklists, and templates
›
Product & Help
Help center, integrations, and updates
›

NISG requirements made easy

The NISG is Austria's new law implementing the EU NIS2 directive. It places high demands on around 4,000 entities in Austria.

A dedicated SECJUR expert builds and runs your certifiable ISMS according to NISG, proactively and with automation. This saves you 80% of the ISMS work and gets you NISG-compliant fast.

✓
ISO 27001 certified
✓
Hosted in Germany
✓
GDPR-compliant
Your SECJUR expert
Tender
IT framework contract
Procurement
Eligibility criteria
met
NISG evidence
available
Security questionnaire
answered
✓
Internal audit scheduled
78 %
NISG progress
NISG Austria

SECJUR customers are in good company

OTTOStahlwerk ThüringenNordzuckeryfoodStadtwerke CottbusSteyr MotorsStatista
Otto DörnerStahlwerk ThüringenNordzuckeryfoodStadtwerke CottbusSteyr MotorsStatista1KOMMA5°Westconnect
Why SECJUR

Your path to NISG compliance

Without SECJUR
Build know-how yourself or buy expensive consulting days
Your team works on it alongside day-to-day business
Lengthy setup, every document from scratch
Risk of failing an inspection
Documentation scattered across Word, Excel, and SharePoint
With SECJUR
Expert Managed
A SECJUR expert builds and runs your NISG risk management
We take on 80% of the ISMS tasks
NISG-compliant faster thanks to automation
Gaps are closed before the authority's inspection
Everything audit-proof and clear on our platform
How It Works

Expert quality at AI speed

Software and expertise in one. You provide information, approve, and involve your organization.

✓
We take on 80% of the ISMS tasks
Get finished, ready-to-use compliance results
✓
Your SECJUR expert makes the decisions
Processes and controls tailored to the way you work
✓
You approve and go into the audit prepared
We take care of the internal audit and management review
Nordzucker
How Nordzucker achieved NIS2 compliance with SECJUR within one week
↗
Digital Compliance Office with your SECJUR expert
Why NISG

Your ticket to more tenders

From 1 October 2026, the NISG imposes risk management, reporting, and supply chain obligations on essential and important entities in Austria. Many public and private clients now require proof of information security from their suppliers. Without documented measures, you are out before price and performance even come into play.

✓
Tenders that were previously closed to you
Public contracts, framework agreements, corporations with strict supplier requirements
✓
Security questionnaires go faster
Most answers are already in your NISG risk management. Your SECJUR expert helps with the rest.
✓
Shorter supplier reviews by your customers
With documented NISG measures, IT security and procurement have fewer follow-up questions.
NISG proof of cybersecurity measures
The comparison

SECJUR compared

Traditional consulting, pure compliance software, or SECJUR: how the three paths to your management system differ.

Traditional consulting
External consultants at day rates
Compliance software
Do-it-yourself platform
SECJUR Expert Managed
Platform plus dedicated expert
Who does the work
– The consultant delivers documents, your team implements
– Your team does everything itself
✓Your expert takes on 80% of the ISMS tasks
Expertise
– High, but limited to the project
– In-house know-how required
✓Dedicated expert who knows your industry
Cost
– Day rates, hard to plan
– License plus high internal effort
✓Predictable package prices
Fit
– Individual, but time-consuming
– Standard templates, often with overhead
✓Only the processes that make sense
Documentation
– Scattered across Word, Excel, and SharePoint
– Centralized in the software
✓Centralized in the DCO, linked and versioned
Ongoing operations
– Project ends, knowledge leaves
– Maintenance stays with you
✓Your expert improves continuously
Evidence
– Depends on the consultant
– Depends on your team
✓Evidence available centrally whenever authorities or customers ask
Success stories

What our customers say

“SECJUR enables us to implement all NIS2 requirements on a single platform. This allowed us to create a centralized, scalable policy system for NIS2 within a week, which can now be rolled out across all European plants.”

Michael Dohr
Michael Dohr
Manager IT Security, Nordzucker AG
Read Case Study

“With SECJUR, we have found exactly what we were looking for in the area of data protection: a data protection-as-a-service package that is ideally suited to us and meets our requirements in every respect through the combination of a team of experts with the online platform Digital Compliance Office.”

Nina Miller
Nina Miller
Global Compliance Officer EMEA/APAC, Yunex Traffic
Read Case Study

“We were able to create our policies extremely quickly with just a few clicks. There was minimal need for further editing, which saved us a lot of time for the technical implementation.”

Stephan Schmidt
Stephan Schmidt
Co-founder and Security Engineer, purple22
Read Case Study
FAQ

Frequently asked questions

Request a Quote →
Who has to comply with the NISG?
+

The NISG implements the NIS2 directive in Austria (Federal Law Gazette I No. 94/2025, in force since 1 October 2026) and applies to essential and important entities, for example in energy, healthcare, transport, digital infrastructure, and public administration. This affects an estimated 4,000 entities in Austria (for comparison: around 30,000 in Germany under the NIS2UmsuCG).

What exactly does the NISG require from us?
+

The NISG requires risk management measures (Section 32 NISG), reporting of significant security incidents to the Federal Office for Cybersecurity (Section 34 NISG), and due diligence obligations towards your supply chain. Your SECJUR expert builds and runs these processes with you.

What deadlines apply under the NISG?
+

Registration with the Federal Office for Cybersecurity by 31 December 2026, a mandatory self-declaration under Section 33 NISG by 1 October 2027, and from 1 October 2028 the authority can order evidence or audits.

What happens in the event of a violation?
+

The NISG provides for supervisory measures by the competent authority.

What internal resources do I need?
+

We take on 80% of the ISMS tasks. You need an internal coordinator and specialist departments that implement the technical and organizational measures.

Isn't compliance software enough?
+

The requirements are the same for all affected entities, from mid-sized companies to large corporations. Your expert works with you to determine which measures, reporting channels, and evidence fit your company and will stand up to supervision.

Get started

Buy results instead of compliance tools and consulting hours

Request a QuoteHow It Works
NISG with SECJUR
Your expert does 80%
Request a Quote